A private S3 origin.
A controlled edge.
Self-directed demo · Not deployedA Terraform reference for serving one static page through HTTPS with CloudFront while S3 blocks public access. The configuration keeps the origin private and permits object reads only from the CloudFront distribution.
Reference architecture
CloudFront uses Origin Access Control to sign requests to the encrypted, versioned S3 bucket. S3 public access block remains enabled.
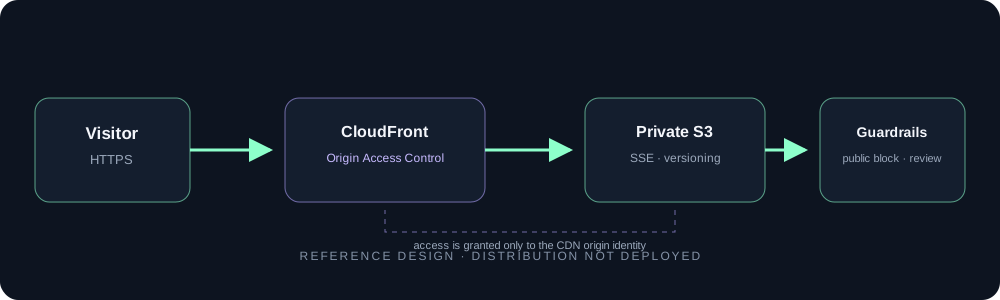
Included safeguards
- All four S3 public access block settings enabled.
- Server-side encryption and bucket versioning.
- CloudFront Origin Access Control with SigV4 signing.
- Bucket policy restricted to read-only access from this distribution.
- HTTP requests redirected to HTTPS.
Implementation checklist
- Review provider versions, IAM permissions and region.
- Inspect the plan and calculate costs before applying.
- Verify HTTPS and access through CloudFront.
- Confirm a direct anonymous S3 request is denied.
- Destroy the test resources and confirm cleanup.
Cost and scope boundaries
This template was not applied to AWS. CloudFront requests, data transfer and S3 usage can incur charges; free-tier terms change and are not guaranteed here. It intentionally omits DNS, custom domains, WAF, access logs and analytics. Terraform state can contain infrastructure details, so store it privately and never upload state or credentials.
Demo limitations: no live distribution, performance numbers, cost measurements, client use or security certification is claimed.