A secure foundation
for a small team.
Self-directed demo · No client deploymentDesign a small Azure network foundation with clear subnet boundaries and an explicit inbound rule. The included Bicep template creates only network resources, so the sample avoids compute and monitoring services that can add recurring costs.
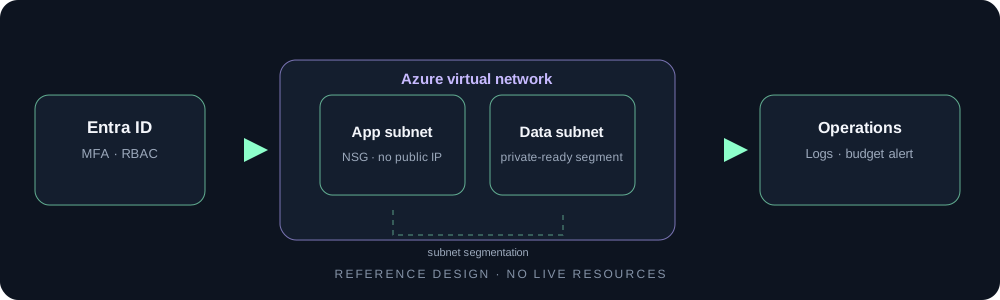
Reference architecture
Entra ID and role assignments are operating controls shown for context; this template does not create identity objects, workloads, logging services or budgets.
What the files implement
- Virtual network with configurable address ranges.
- App and data subnets for a clear segmentation starting point.
- NSG association on the app subnet and an explicit deny rule for inbound Internet traffic.
- Outputs for the network and NSG resource IDs.
Build and validate
- Review the Bicep source and select an unused CIDR range.
- Validate and inspect the proposed resource changes.
- Apply only in an approved non-production subscription.
- Confirm subnet and NSG associations; verify no compute or public IP was created.
- Remove the demo resource group and record cleanup.
Security and cost boundaries
This is a template, not proof of a completed cloud deployment. No cloud resources were created for this portfolio. The sample omits VMs, public IPs, Log Analytics and paid monitoring; still review current Azure pricing, policy and your deployment preview before applying it. Use least-privilege roles and never publish tenant or subscription identifiers.