Test with permission.
Report with evidence.
Training workflow · No assessment findings claimedA safe local workflow for practicing assessment planning, minimal evidence capture and remediation retesting against an intentionally vulnerable training app. The sample Compose file binds the service to loopback only.
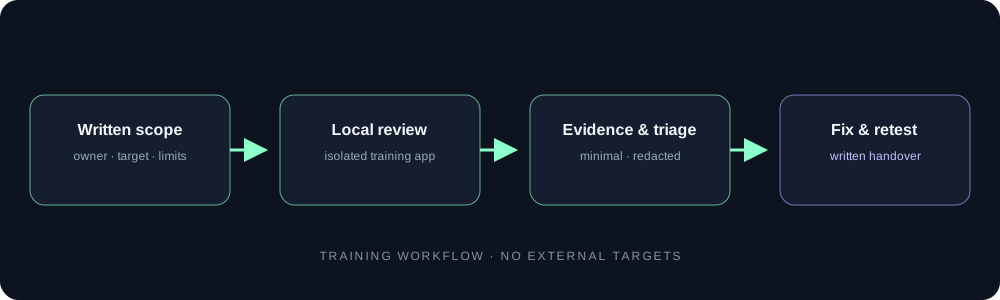
Scope-to-handover workflow
Lab guardrails
- Training target is intentionally vulnerable; keep it on the local machine.
- Port mapping is restricted to
127.0.0.1:3000. - No external targets, tunnels, port forwards or destructive tests.
- Written authorization and a stop condition are required for any client assessment.
- Keep evidence local and redact tokens, personal data and private identifiers.
Assessment workflow
- Complete the scope worksheet and confirm authorization.
- Start the local target and confirm loopback-only binding.
- Perform bounded manual review within the written scope.
- Record only issues actually reproduced; leave unverified claims out.
- Document remediation, retest and clean up the local lab.
What is in the kit
Docker Compose file, authorization and scope worksheet, evidence-handling notes, blank report template and cleanup guidance. The report template contains no invented findings. This project describes a training workflow and is not a claim that a VAPT engagement was performed.
Only assess systems you own or have explicit written permission to test. Stop if the target, scope or authorization is unclear.